Raw biometric data never leaves a user’s device
All encryption happens directly on the smartphone before transit.
VeryAI is now Very.
Very is designed to be privacy-first. We were born to create an authentic internet without sacrificing your most sensitive data.
We believe that you should not have to sacrifice your privacy or share governmental information to prove you’re a real person.
All encryption happens directly on the smartphone before transit.
Palm Models are irreversible and they cannot be reverse-engineered back into a palm image.
Very works with frontier researchers to stay ahead of the latest deepfakes and generative scams.
When a new user registers and scans their palm, Very converts their features into an encrypted Palm Model directly on the user’s smartphone.
Our position
Biometrics, not KYC.
Upload a government ID
Not required
Palm check
 Verified human
At registration, users scan their palm multiple times either within a platform through the Very SDK or within the Very app. That scan is converted into a mathematical Palm Model and stored on encrypted servers. When a user is asked to reverify their palm, it is once again converted into a Palm Model and compared against the original version.
All biometric data is encrypted using AES-256, both at rest and in transit.
The data Very collects can be permanently deleted by the user in the “Settings” menu of the Very app.
Platforms never receive raw biometric data or the Palm Model. Instead, they get a pass or fail state from Very, as well as a platform-specific VeryID.
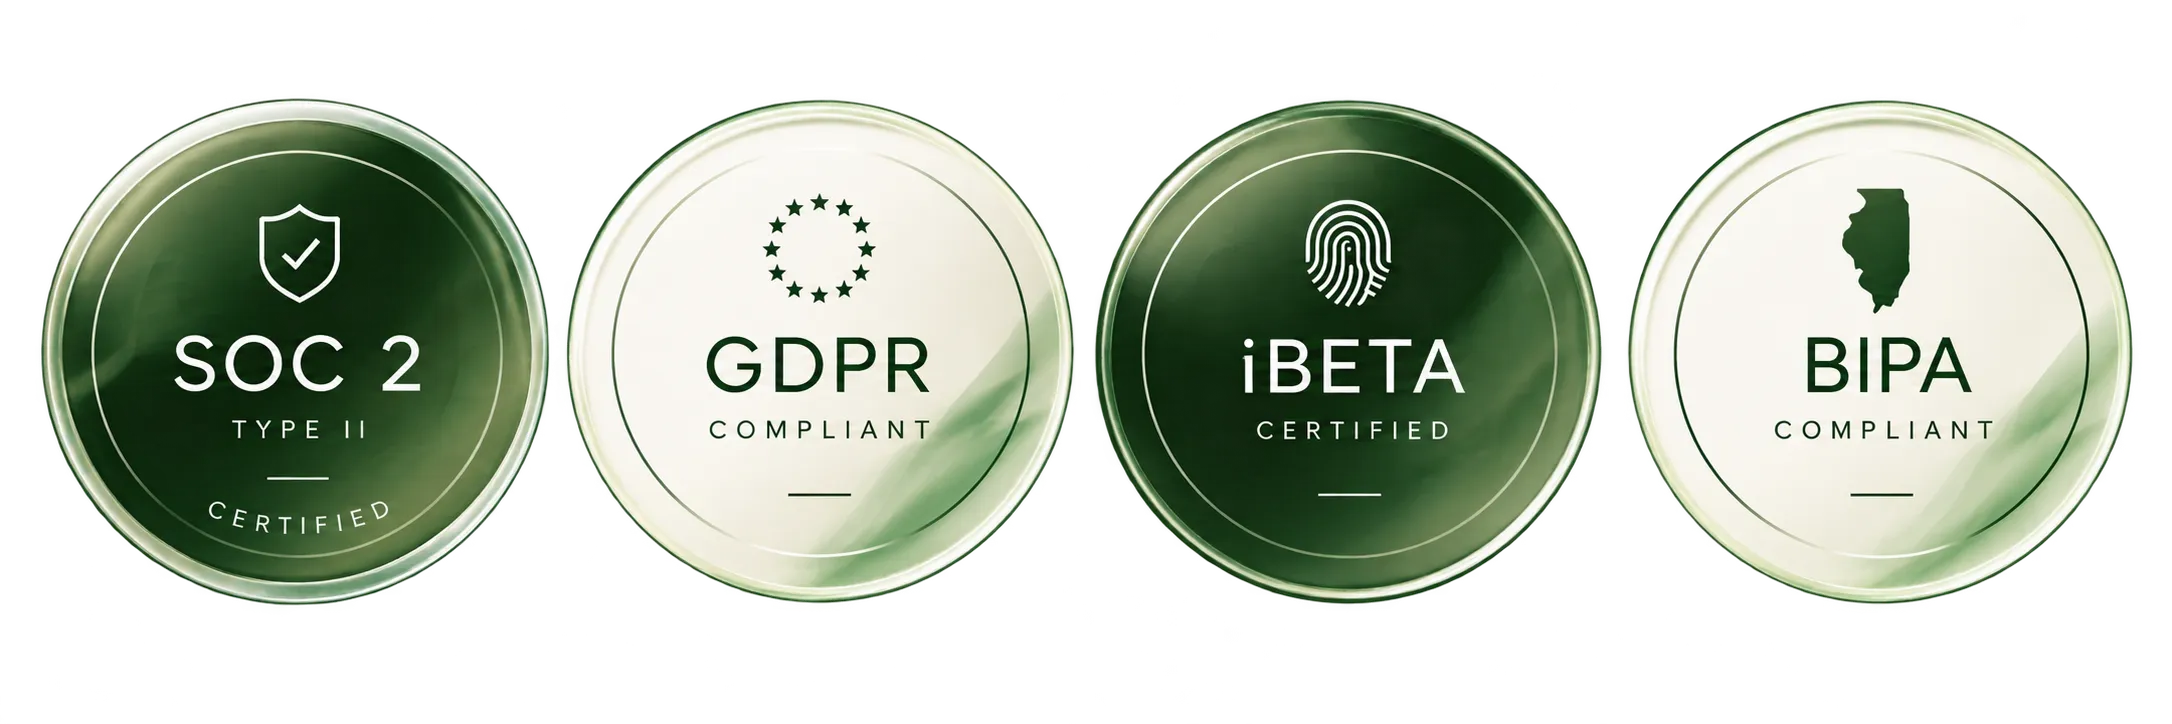
Yes, Very follows the EU General Data Protection Regulation (GDPR) for all personal data we process:
Business customers can also sign our Data Processing Agreement (DPA). For more details, read our Privacy Policy or email legal@very.org. We have also appointed a Data Protection Officer, reachable at dpo@very.org.
In the event of a security incident, we will notify you in accordance with Article 34 GDPR, UK GDPR, and applicable state notification laws. Where legally required, we will also notify the relevant supervisory authority.
The only data stored on the device is the local biometric template. Raw, high-resolution palm images are deleted immediately. Only encrypted data is stored on Very’s servers: the encrypted Palm Model, the VeryID user identifier, last-activity signals like recent logins, session ID, and other session artifacts, and low-resolution copies of palm images, which are held for 90 days for audit purposes.
For users, the same user VeryID can be used across multiple platforms that use Very. A user’s VeryID is linked to their palm, not any specific account.
To protect privacy, client-side IDs that are sent to platforms change every session.